Search the Community
Showing results for 'Quick Launch Keyboard'.
Found 1785 results
-
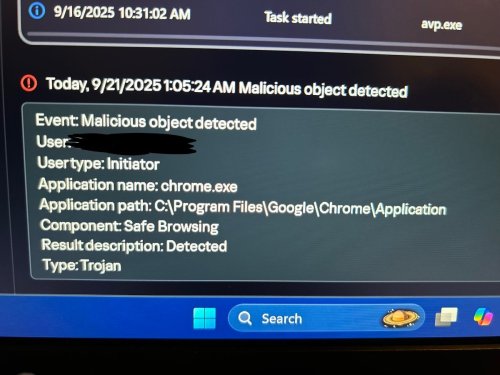
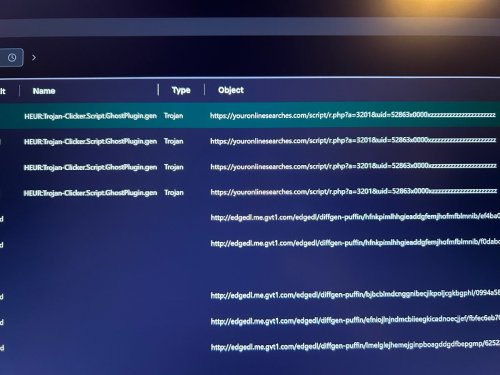
 Blinx posted a topic in Virus and Ransomware related questionsHey everyone, Tonight when I search on Google via chrome, 3 times I’ve had below pop up, I’ve never seen it before: HEUR:Trojan-Clicker Script GhostPlugin.gen It tells me it’s a Trojan type and that the object is: https://youronlinesearches.com/script/r.php?a=3201&uid=52863x0000xzzz7. ZZZZZZZZZ However Kaspersky tells me that it has blocked the download each time, this while I’m on Google via chrome, I’ve never seen this before and the only sites I go on are legit ones. I have done a quick scan and it comes back with nothing found, Kaspersky tell me: Event: Malicious object detected User: ***** (I’m not inc this for privacy) Usertype: Initiator Application name: chrome.exe Application path: C:\Program Files|Google|Chrome/Application Component: Safe Browsing Result description: Detected Type: Trojan Can anyone help?
-
 Hello @openurwindow, Welcome! Quick Startup has a *limited* list of applications because it's *only* those apps that are starting at boot time -> Kaspersky has designed the Quick Startup tool to enable users to disable any apps in the list that are not essential & or not run daily, that's why it says: Speed up computer at start-up -> please read: Quick Startup. In (your) computer - is there an application that's starting at start-up, that's not listed ? IF 'yes', please provide more details, name of the app, version? Which Kaspersky software version? On Windows taskbar *hidden icons*, rightclick the Kaspersky icon, select About? Which Windows 10 & Build, in Windows Search, type WINVER, select the app & post back the winver information please? The change that (you're) proposing would need to be submitted via a Feedback, I have a suggestion OR I have a complaint *but* first, let's try to understand a little more about the issue by providing more information please? Please post back? Thank you? Flood?+?
-
 svc_kms posted a blog entry in Kaspersky Security Center's Kaspersky Security Center CommunityProblem Description, Symptoms & Impact The installation of the Network Agent isn't possible on a device because of the error System error 0x1F (A device attached to the system is not functioning.) Diagnostics In the MSI Log and Application Eventlog can be found the following line: (1192/0x0 ("System container 'LOC-PUB-6EEB50F8D2EB46029DB4CCB77E0DA651' is corrupt") Workaround & Solution The issue comes from a corrupt cryptostorage in the OS. It's not a KL related issue, although there is a possible solution to fix it. On the problem host launch cmd.exe with administrative privileges Run klcryptstgclean.exe: klcryptstgclean -tl 4 -tf $klcryptstgclean_trace.txt -l klcryptstgclean.log Try to install NAgent. If it doesn't help, perform actions from the Cryptostorage-1.docx file. If installation fails again, send to Kaspersky Support the following files: "$klcryptstgclean_trace.txt", "klcryptstgclean.log", new GSI with klnagent installation logs. It is not KSC and klnagent related issue. It is OS related issue. If workaround doesn't help, try sfc /scannow command, OS restore, OS reinstallation or contact MS support.
-
svc_kms posted a blog entry in Kaspersky Security Center's Kaspersky Security Center CommunityAdvice and Solutions (Forum Knowledgebase) Disclaimer. Read before using materials. The article is giving a working configuration instructions for domain authentication by using NTLM and Kerberos protocols. NOTE: Domain authentication in OpenAPI over Kerberos protocol has the following restrictions: Administration Server address must be specified exactly as the address for which the Service Principal Name (SPN) is registered for domain account name. In the domain, you need to set the Service Principal Name (SPN) to publish the OpenAPI service on port 13299 for the machine with the Administration Server, the service of which is running under the name of the domain user <domain-user>. Kaspersky Security Center 13 Web Console user must be authenticated in Active Directory by using Kerberos protocol. Kerberos authentication should be allowed in web-browser. For details, refer to documentation of used web-browser. Details SPN - Service Principal Name Log in Domain Controller as Domain administrator. Open powershell as admin and run the following commands: Powershell setspn.exe -A HTTP/hostname-node-1.domain.local -u domain\user-ksc-service setspn.exe -A HTTP/hostname-node-2.domain.local -u domain\user-ksc-service Example setspn.exe -A HTTP/kscw-node-1.sales.lab -u sales\ksc setspn.exe -A HTTP/kscw-node-2.sales.lab -u sales\ksc setspn.exe -L -u sales\ksc #command for check spn records #Response Registered ServicePrincipalNames for CN=KSC Service,CN=Users,DC=sales,DC=lab: HTTP/kscw-node-1.sales.lab HTTP/kscw-node-2.sales.lab Enable Kerberos/NTLM authentication in web browsers Microsoft Edge \ Internet Explorer win + r => inetcpl.cpl Activate the Security tab. Select Local intranet and click Sites. In the opened dialog box click Advanced. Add the host name of Adaxes Web interface (e.g. host.company.com). Click Close and then click OK. Click Custom level. Navigate to Scripting and enable Active scripting. Navigate to User Authentication \ Logon. Select Automatic logon only in Intranet zone and click OK. Activate the Advanced tab. In the Settings list, navigate to the Security section. Select Enable Integrated Windows Authentication and click OK. Mozilla Firefox - https://developer.mozilla.org/en-US/docs/Mozilla/Integrated_authentication Launch Mozilla Firefox In the URL window, enter about:config and press Enter. In the filter text box, enter network.negotiate. Double-click the network.negotiate-auth.trusted-uris option and enter the host name of Adaxes Web interface (e.g. host.company.com). Repeat previous step for the network.negotiate-auth.delegation-uris option. Google Chrome Add the Software\Policies\Google\Chrome\AuthServerWhitelist key equal to *.<domain-name>.local to the registry Add the Software\Policies\Google\Chrome\AuthNegotiateDelegateWhitelist key equal to *.<domain-name>.local to the registry
-
svc_kms posted a blog entry in Kaspersky Hybrid Cloud Security's Kaspersky Hybrid Cloud SecurityPrerequisetes: Supported vSphere by Kaspersky Agentless solution Usage of NSX version 3.2+ Deployed Kaspersky Agentless 6.1 Antivirus or/and Network Attack Blocker Appliance Problem Anew registration and Kaspersky Agentless 6.1 Antivirus or/and Network Attack Blocker Appliance deployment completes successfully. By attempt to create Service Profile for Kaspersky Agentless 6.1 Antivirus or/and Network Attack Blocker fails with error AntiVirus and Network Attack service registration might fail with the error "Service Definition id <ID> <Kaspersky Component> not found in MP Root cause NSX-T does not delete service references of Kaspersky Agentless 6.1 Antivirus or/and Network Attack Blocker Appliance Solution Through terminal like putty you need access to NSX-T appliacnce and launch the command curl -kG https://admin:<PASSWORD>@<nsx-t address>/policy/api/v1/infra/service-references The path value should be remembered for Kaspersky File Antimalware Protection and for Kaspersky Network Protection Delete service reference by path value by launching the command curl -kX DELETE https://admin:<PASSWORD>@<nsx-t address>/policy/api/v1/<value of path> After it delete previously created profile service for Kaspersky Agentless 6.1 Antivirus or/and Network Attack Blocker and create it anew
-
svc_kms posted a blog entry in Kaspersky Hybrid Cloud Security's Kaspersky Hybrid Cloud SecurityTo achieve this goal for Kaspersky Agentless 6.1 solution you should: Shutdown Kaspersky Agentless Appliance Disable the option "Сonfigure/vApp Options/edit/OVF Details/OVF environment transport/ISO image" for Kaspersky Agentless Appliance Launch Kaspersky Agentless Appliance
-
svc_kms posted a blog entry in Kaspersky Endpoint Security's Kaspersky Endpoint SecurityProblem Sometimes Anti-Cryptor task in KESL won't be able to launch after the OS is started. This may happen because Anti-Cryptor needs all the protected network resources to be up before KESL service is started. In other words, Samba or NFS services should be started before KESL service. Solution To resolve this problem you need to make sure that services start in the correct order. For Systemd systems: 1. Create a file /etc/systemd/system/kesl.service.d/override.conf # touch /etc/systemd/system/kesl.service.d/override.conf 2. Add the following to /etc/systemd/system/kesl.service.d/override.conf: [Unit] After=nfs-server.service smb.service [Service] TimeoutSec=300 3. Reload services # systemctl daemon-reload For Sys V init systems: Rename Samba and NFS init files to make those services start earlier. E.g. # mv /etc/rc3.d/<smb_init_file> /etc/rc3.d/S49smb # mv /etc/rc3.d/<nfs_init_file> /etc/rc3.d/S49<nfs_init_file> Where <smb_init_file> and <nfs_init_file> stand for current init files present in the system. NFS init file may have different name depending on your environment - nfs, nfs3 or nfs-server.
-
svc_kms posted a blog entry in Kaspersky Hybrid Cloud Security's Kaspersky Hybrid Cloud SecuritySNMP daemon on SVM should have the following default settings: protocol version: v2c rocommunity name: public listening address and port: 0.0.0.0:161 access type: read only transport: UDP logging: syslog The following statistics can be received from SVM: # Description Name Identifier 4.1 CPU Statistics UCD-SNMP-MIB::systemStats 4.2 Memory Statistics UCD-SNMP-MIB::memory 4.3 Load average statistics UCD-SNMP-MIB::laTable 4.4 Disk statisitcs HOST-RESOURCES-MIB::hrStorageTable 4.5 Network statistics IF-MIB::ifTable 4.7 Amount of desktop VMs connected KSVLA-MIB::ksvlaProtectedDesktopCount 1.3.6.1.4.1.23668.1491.1539.1.1 4.8 Amount of server VMs connected KSVLA-MIB::ksvlaProtectedServerCount 1.3.6.1.4.1.23668.1491.1539.1.0 4.9 ODS running status: - in progress (if all ODS Tasks are running) - waiting (if at least one ODS task is waiting for processing) - none (if no ODS tasks are running/waiting at all) KSVLA-MIB::ksvlaODSStatus 1.3.6.1.4.1.23668.1491.1539.0.0 4.10 ODS queue lenght: amount of VMs awaiting ODS processing KSVLA-MIB::ksvlaODSQueueLenght 1.3.6.1.4.1.23668.1491.1539.0.1 4.11 Amount of simualtaneously running ODS tasks KSVLA-MIB::ksvlaODSTaskCount 1.3.6.1.4.1.23668.1491.1539.0.2 4.12 Current percent of an allowed physical memory consumption - In case of watchdog is on use WDSERVER_MAX_MEM const from ScanServerLaunch.sh as maximum - In case of watchdog is off use 100% as maximum KSVLA-MIB::ksvlaMemoryConsumption 1.3.6.1.4.1.23668.1491.1539.3.0 4.13 Current percent of an allowed swap consumption - In case of watchdog is on use WDSERVER_MAX_SWAP const from ScanServerLaunch.sh as maximum - In case of watchdog is off use 100% as maximum KSVLA-MIB::ksvlaSwapConsumption 1.3.6.1.4.1.23668.1491.1539.3.1 4.14 Main processes state (running/stopped): -- scan server daemon KSVLA-MIB::ksvlaScanServerStatus 1.3.6.1.4.1.23668.1491.1539.2.0 -- klnagent daemon KSVLA-MIB::ksvlaKlnagentStatus 1.3.6.1.4.1.23668.1491.1539.2.1 -- nginx daemon KSVLA-MIB::ksvlaNginxStatus 1.3.6.1.4.1.23668.1491.1539.2.2 -- watchdog KSVLA-MIB::ksvlaWatchdogStatus 1.3.6.1.4.1.23668.1491.1539.2.3 Change SNMP community name Edit file /etc/snmnp/snmpd.conf Change public into the string recommunity on your own Save changes Restart SNMP daemon - systemctl restart snmpd Move on SNMPv3 Stop SNMP daemon - systemctl stop snmpd Launch the command - net-snmp-config --create-snmpv3-user -ro -a "authpass" -x "privpass" -X AES -A SHA "user" "authpass" is the private key/password for generating HMAC when connecting to snmpd, "privpass" is the private key/password for encrypting snmp traffic, "user" is the username for snmpd. "authpass" and "privpass" we can say passwords, which should be generated by you own "user" - user name for snmpd This command will make mpdifications into two files - /etc/snmp/snmpd.conf and /var/lib/net-snmp/snmpd.conf Restart SVM
-
"The specified path does not exist" error appears by launching any executable file [KSV Light Agent]
svc_kms posted a blog entry in Kaspersky Hybrid Cloud Security's Kaspersky Hybrid Cloud SecurityProblem Environment: Citrix Virtual Apps and Desktops (Citrix XenApp and XenDesktop) with enabled option Citrix UPL (User Personalization Layer) Citrix App Layer Non-English Operation System localization. After installation of KSV LA 5.2, you can face the error "The specified path does not exist" which appears by launching any executable file. Possible root cause Both Citrix technologies use separate vhd files for creating VMs by using Citrix App Layer and for roaming profiles used by Citrix UPL. As the result, the merge of vhd files processes and Citrix driver returns incorrect path of where the executable files are. Workaround Install Kaspersky Light Agent 5.2 and ensure it does not connect to SVM. Disable Self Defense and exit LA. Add registry file from this archive. Launch installation of the latest cumulative patch from the archive (all further released Cumulative PFs will contain the fix as well). As soon as LA informs the restart is needed, restart VMs. Connect LA to SVM. Problem should be solved. -
svc_kms posted a blog entry in Kaspersky Endpoint Security's Kaspersky Endpoint SecurityEnvironment/Preconditions KSC - 12 KSWS - 11.0.1.897 You may find a massive increase in disk usage from the folder report under the Kaspersky folder. The size of the report folder will increase from around 2GB to 12GB, the files in the report folder have random name (like 340a13d9-2a50-4c4e-94d6-82a79d80da4b), which rapidly grows and consumes disk space. The file can be deleted to resolve the disk space full issue, which itself can cause many issues (can't log in to the server, KSWS stop, etc) To delete the file: Stop KSWS. Add permission/owner for the login account. Right-click and delete file. This issue is caused by the Task log setting under Log and Notification tab in the KSWS policy. To avoid the detailed events issue: Ensure that there are no Informational events in the Importance level option in each Component. Remove task logs older than (days) is selected. In case you do the above step and the random file is still keep growing rapidly (100 MB per hour), it may be causes by the flooding event. You can check the event flooding by using product local console. Install and launch KSWS tools and under Logs and Notifications node observe Task logs, System audit log and Security log in local UI. Check which event is generated in excessive amounts.
-
-
svc_kms posted a blog entry in Kaspersky Endpoint Security's Kaspersky Endpoint SecurityWhile removing Kaspersky Security for Windows Server Console removal log may contain a message: Error 1336. There was an error creating a temporary file that is needed to complete this installation. Folder: C:\Program Files (x86)\Common Files\Kaspersky Lab\Kaspersky Security for Windows Server\. System error code: 5 And if you launch removal process using an appwiz.cpl a popup will be displayed stating : “There was an error creating a temporary file that is needed to completed this installation” This may happen because KES is installed in the system, so far the workaround is the following: Disable self-defense in KES and perform removal one more time.
-
svc_kms posted a blog entry in Kaspersky Security Center's Kaspersky Security Center CommunityRDP connection invoked via KSC console uses hostname to connect to a host - mstsc.exe is invoked with /v hostname parameter. Edit command line used to invoke mstsc.exe with ip address parameter instead of the hostname: Open Custom tools → Configure custom tools Select Remote Desktop, click Modify Edit Command line text box, it should contain <host_ip> instead of <A>: /v:<host_ip>:<P> /f Disable Create tunnel for TCP port specified below checkbox Administration Console will now launch mstsc.exe with ip address as argument.
-
svc_kms posted a blog entry in Kaspersky Endpoint Security's Kaspersky Endpoint SecuritySecurity administrator can create KSWS Application Control rules based on Digital Certificate. What does product actually checks and how it is related to the file itself? First of all, product checks whether the file matches certificate. Secondly, whether certificate is valid. If any of verifications fail - launch of the file will be denied. And vice versa. If signed file which execution was allowed by certificate has been modified, will execution of the file be allowed? Altering the file signed by the certificate will cause its certificate to no longer confirm the integrity of this file. As a result "Allowing" rule will no longer be applied to the file. How the control of the revoked certificates operates, if such a control exist? Certificates revocation in the operation system is implemented through OS updates. When a certificate becomes revoked, it can no longer pass validation checks. Thus file execution will be blocked. When both the subject of the certificate and its thumbprint verifications are selected, then product checks that the file is signed by an exact "version" of certificate. In other words, it will not be enough to make a self-signed certificate with the Subject field equal to "Redmont, Microsoft" - such a certificate does not coincide with the real thumbprint of Microsoft.
-
 Yashhhh replied to Pandas's topic in Kaspersky Total SecurityI can't launch valorant it says the app doesnt give permission to enable i cant launch valorant while kaspersky is on. It says this app doesn't give permission to open valorant. Please provide a solution
-
 Mouloud replied to WLee's topic in Kaspersky Total SecurityI am using KSC 2021 and I have faced the same issue. When I used the alibaba.com website the “Secure Keyboard input” kicked in when i tried to enter a search. When I shifted to Microsoft Office 2019 applications I noticed that my hardware keyboard froze except for the “enter” and “backspace” keys but remained functional on this website. I chatted with “Support” and after several attempts, they deduced that the issue was related to the website and not Kaspersky. The best solution offered was to exclude this website from the “Secure Keyboard Input” protection. Which we tested. The strange result is that after this, only when I revert to the alibaba.com website and type a search without the “Secure Keyboard Input” protection will my hardware keyboard unfreeze. So I kept the exclusion awaiting a better solution. Then something worst happened. Any time I type on any webpage triggering the “Secure Keyboard Input” and associated popup, my hardware keyboard freezes. Then, only when I reopen the alibaba.com webpage and type a search on it does my hardware keyboard unfreeze on this page and subsequently on other pages and on the Microsoft Office 2019 applications. I use Firefox but the same is valid for Edge. I have serious doubts that this website does not tolerate “Secure Keyboard Input” and may have injected some form of keylogger which is affecting “Secure Keyboard Input” altogether. Any Thoughts?
-
svc_kms posted a blog entry in Kaspersky Security for Mail Server's Kaspersky Security for Mail ServerWhen administrator attempts to establish a connection between KS4O365 workspace and their Exchange online organization by doing the following in the administration console: Office 365 connection → Exchange Online connection → Grant Access → passes the consent validation algorithm but in the end gets the Error processing the request error: This error is usually triggered by the browser settings on the client host that is performing the consent validation. Upon executing consent validation algorithm we get the access token from Microsoft. Then we redirect browser to our web site's URL and attach access token as a cookie. Upon redirecting, cookie with access token is lost/blocked somehow, usually this is caused by one of the following reasons: Browser filters cookies on its own. For instance due to some extensions, browser settings, or due to some beta version of browser with paranoid default security settings. Some 3rd party program, for example a file anti-virus, is blocking access to the file with the browser's cookies on the local hard drive. Thus, the following action plan is suggested. Step-by-step guide Clear all history, cache and cookie in the web-browser, restart it and check the reproduction. If it doesn’t help, then please make sure that the same error occurs if you try to do the same operation in another web-browser supported by the product (https://support.kaspersky.com/KS4MO365/1.2/en-US/141858.htm) or in incognito mode of the browser. Also, temporarily disabling anti-malware solutions or any 3-rd party products that might be blocking/locking/inspecting browser's cookie files is called for. If the issue will persist, then please do the following: 1. Open Google Chrome web-browser. 2. Press F12 keyboard button. 3. Enable Preserve log option in Network tab. 4. Reproduce the whole scenario from the begging (log into business hub account) and the issue itself. 5. Make an error screenshot with time stamp. 6. Export Network debugging results to HAR-file. 7. Provide HAR-file + screenshot to the Kaspersky Support. Also we will be interested in the URL that will be shown when the error will pop-up in the browser.
-
 Psiu47 posted a topic in Kaspersky: Basic, Standard, Plus, PremiumGreetings once more. It have been a wild in the past months holding onto KS 21.21.7.384(a) bugged version and hoping for a future version to address the issues that I have listed in the past. However as the sutomatic system that execute these installation and convert the prévios Kaspersky protection to a newer version comes always along with another to address. The welcome / front page of the interface next to 🟢 shield. The message previously showed the followed message: "Vírus/malware detection is active" Now the Reading It says a duplicate message as It reads: "Main protection components are running/ are active". Meanwhile going to Security tab ro check all protection components, the reading still show "All components are active". I mean these phrases are becoming repetitive and unwelcome. Also there is on troubling problem with mouse quick Scan prompt menu where It Will bring now a duplication of KS rundown. I was avoiding to install my previous KS 21.21 because I've suspected there would bem another version comming out anytime soon. With KS 21.22 install applied. Do I have to fully unistall and fresh download from My Kaspersky This version to repair this KS mouse Scan duplication? Or should I wait as I've been waiting for months to get a proper fiz for KS 21.21 major issues?

-
Psiu47 replied to Psiu47's topic in Kaspersky: Basic, Standard, Plus, PremiumP.S. It seems that I have missjudged the issues with quick mouse scan. I have restarted my Wind.11 23h2 like a normal restart and I ran the action with the mouse to any icon on screen and the problem didnt appear. But I will keep monitoring for bugs, abnormal symptoms.

-
 Kaspersky Security Services is a suite of professional offerings provided by Kaspersky to help businesses and individuals maximize cybersecurity defenses and minimize risks. Below is an overview of these services: 1. Kaspersky Professional Services Tailored for businesses, this includes deployment, configuration, and optimization of Kaspersky solutions to align with the organization’s specific security policies and IT environment. Implementation Services: For smooth deployment of Kaspersky products like Security Center, Endpoint Security, and more. Health Checks: Ensure the Kaspersky solution is optimally configured and running efficiently. Migration Services: Seamlessly upgrade or migrate between Kaspersky versions or platforms. Custom Integration: Adapt Kaspersky solutions to integrate with other IT systems. 2. Managed Security Services (MSS) A subscription-based model where Kaspersky oversees and manages security for businesses. Threat Monitoring and Incident Response: 24/7 monitoring, threat detection, and remediation by Kaspersky experts. SOC-as-a-Service: A cloud-based Security Operations Center tailored to SMEs. Endpoint Detection and Response (EDR): Active protection against advanced threats targeting endpoints. 3. Cybersecurity Training and Awareness Programs aimed at enhancing cybersecurity skills and awareness for IT teams and employees. Security Awareness Training: Courses to reduce the risk of human errors, such as phishing attacks. Cybersecurity Certification Programs: For IT professionals managing Kaspersky solutions. 4. Incident Response and Forensics Kaspersky provides post-incident support to contain breaches, analyze root causes, and help recover systems. Emergency Incident Response: Quick reaction to active cyberattacks to minimize damage. Digital Forensics Services: Investigating cyber incidents and collecting actionable evidence. 5. Threat Intelligence Services Access to Kaspersky’s global threat intelligence data for advanced insights into the threat landscape. API Integrations: Feed real-time threat data into SIEM or SOAR platforms. Tailored Threat Intelligence Reports: Insights into regional or sector-specific cyber threats. APT Intelligence: Detailed analysis of Advanced Persistent Threats. 6. Penetration Testing and Vulnerability Assessment Comprehensive evaluations of your security infrastructure to identify vulnerabilities. Penetration Testing: Simulating real-world attacks to test defenses. Vulnerability Assessments: Scanning and analyzing systems for weak points. 7. Data Protection Services Help businesses achieve compliance with data protection regulations (e.g., GDPR) and secure sensitive information. Data Loss Prevention (DLP): Implement strategies to prevent unauthorized data leakage. Encryption Services: Ensure data remains safe even if devices are lost or stolen. 8. Cloud Security Services Secure cloud workloads and hybrid environments with dedicated solutions. Public and Private Cloud Security: Solutions for Microsoft Azure, AWS, Google Cloud, etc. Cloud Workload Protection: Secure virtual machines, containers, and storage. 9. Threat Hunting Services Proactively seek out hidden threats that may bypass traditional defenses. Proactive Threat Hunting: Expert-driven analysis using Kaspersky tools. Customized Detection Rules: Tailored rules for detecting anomalies in your systems. 10. Compliance and Risk Assessment Services Support organizations in meeting regulatory requirements and reducing overall security risks. Compliance Gap Analysis: Identify gaps in adherence to frameworks like ISO 27001, PCI DSS, and others. Risk Assessment: Holistic evaluation of your IT infrastructure’s security posture.
-
 Hori9163 replied to tl2152's topic in My KasperskyI was locked out of several accounts because I couldn’t receive SMS on my old number, which no longer works. Needed a quick way to get verification codes without relying on my carrier. Used another mobile service — picked a UK number directly in the browser, no registration. The code arrived in under two minutes. Since it’s a real SIM-based number, not VoIP, it worked with services that usually block virtual lines. Didn’t have to install an app or reactivate a physical SIM.
-
 redcat2025 replied to redcat2025's topic in Virus and Ransomware related questionsdid the steps but same problem and same massage: Prevented downloading of software that can be used by criminals "Some legitimate software can damage your computer if it is used by criminals. Hence, we prevent downloading of remote control programs, auto-dialers, adware, and some other legitimate software. You were protected from downloading this program by Kaspersky security. You can close this window with no risk. Hide details Detected at: 6/20/2025 8:35:32 PM Web address: https://eztvx.to/home Reason: contains adware, auto-dialers, legitimate software that can be used by criminals to damage your computer or personal data Application: not-a-virus:HEUR:AdWare.Script.Redirect.gen " adware clean. this is a new log: # ------------------------------- # Malwarebytes AdwCleaner 8.5.1.601 # ------------------------------- # Build: 03-26-2025 # Database: 2025-04-04.3 (Cloud) # Support: https://www.malwarebytes.com/support # # ------------------------------- # Mode: Scan # ------------------------------- # Start: 06-20-2025 # Duration: 00:00:11 # OS: Windows 11 (Build 22631.5472) # Scanned: 32087 # Detected: 35 ***** [ Services ] ***** No malicious services found. ***** [ Folders ] ***** No malicious folders found. ***** [ Files ] ***** No malicious files found. ***** [ DLL ] ***** No malicious DLLs found. ***** [ WMI ] ***** No malicious WMI found. ***** [ Shortcuts ] ***** No malicious shortcuts found. ***** [ Tasks ] ***** No malicious tasks found. ***** [ Registry ] ***** No malicious registry entries found. ***** [ Chromium (and derivatives) ] ***** No malicious Chromium entries found. ***** [ Chromium URLs ] ***** No malicious Chromium URLs found. ***** [ Firefox (and derivatives) ] ***** No malicious Firefox entries found. ***** [ Firefox URLs ] ***** No malicious Firefox URLs found. ***** [ Hosts File Entries ] ***** No malicious hosts file entries found. ***** [ Preinstalled Software ] ***** Preinstalled.HPAudioSwitch Folder C:\Program Files (x86)\HP\HPAUDIOSWITCH Preinstalled.HPAudioSwitch Registry HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{BE7019B0-DF32-4A1C-B44F-4AC62685CD25} Preinstalled.HPAudioSwitch Registry HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\HPAudioSwitch Preinstalled.HPAudioSwitch Task C:\Windows\System32\Tasks\HPAUDIOSWITCH Preinstalled.HPCoolSense Folder C:\Program Files (x86)\HP\HP COOLSENSE Preinstalled.HPCoolSense Folder C:\Users\Pixel-PC\AppData\Local\HP\HP COOLSENSE Preinstalled.HPCoolSense Folder C:\Windows\System32\Tasks\HP\HP COOLSENSE Preinstalled.HPCoolSense Registry HKLM\Software\Classes\CLSID\{224695A4-BD5E-4C38-B354-A4C828E61BF7} Preinstalled.HPJumpStartApps Folder C:\Program Files (x86)\HP\HP JUMPSTART APPS Preinstalled.HPJumpStartApps Registry HKLM\Software\Wow6432Node\\Microsoft\Windows\CurrentVersion\Uninstall\HP JumpStart Apps Preinstalled.HPJumpStartBridge Folder C:\Program Files (x86)\HP\HP JUMPSTART BRIDGE Preinstalled.HPJumpStartLaunch Folder C:\Program Files (x86)\HP\HP JUMPSTART LAUNCH Preinstalled.HPJumpStartLaunch Registry HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{0B3EB0F5-EE46-4F08-B2BA-057B6F86AB15} Preinstalled.HPJumpStartLaunch Registry HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\HPJumpStartLaunch Preinstalled.HPJumpStartLaunch Task C:\Windows\System32\Tasks\HPJUMPSTARTLAUNCH Preinstalled.HPRegistrationService Folder C:\Program Files (x86)\HP\HP REGISTRATION SERVICE Preinstalled.HPRegistrationService Folder C:\ProgramData\HP\HP REGISTRATION SERVICE Preinstalled.HPSupportAssistant Folder C:\HP\SUPPORT Preinstalled.HPSupportAssistant Folder C:\Program Files (x86)\HEWLETT-PACKARD\HP CUSTOMER FEEDBACK Preinstalled.HPSupportAssistant Folder C:\Program Files (x86)\HEWLETT-PACKARD\HP SUPPORT FRAMEWORK Preinstalled.HPSupportAssistant Folder C:\Program Files (x86)\HEWLETT-PACKARD\HP SUPPORT SOLUTIONS Preinstalled.HPSupportAssistant Folder C:\ProgramData\HEWLETT-PACKARD\HP SUPPORT FRAMEWORK Preinstalled.HPSupportAssistant Folder C:\Users\Pixel-PC\AppData\Local\HEWLETT-PACKARD\HP SUPPORT FRAMEWORK Preinstalled.HPSupportAssistant Folder C:\Users\Pixel-PC\AppData\Roaming\HEWLETT-PACKARD\HP SUPPORT FRAMEWORK Preinstalled.HPSupportAssistant Folder C:\Windows\System32\config\systemprofile\AppData\Local\HEWLETT-PACKARD\HP SUPPORT FRAMEWORK Preinstalled.HPSupportAssistant Registry HKLM\Software\Classes\CLSID\{E76FD755-C1BA-4DCB-9F13-99BD91223ADE} Preinstalled.HPSupportAssistant Registry HKLM\Software\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{E76FD755-C1BA-4DCB-9F13-99BD91223ADE} Preinstalled.HPSupportAssistant Registry HKLM\Software\Wow6432Node\\Classes\CLSID\{E76FD755-C1BA-4DCB-9F13-99BD91223ADE} Preinstalled.HPSupportAssistant Registry HKLM\Software\Wow6432Node\\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{E76FD755-C1BA-4DCB-9F13-99BD91223ADE} Preinstalled.HPSupportAssistant Registry HKLM\Software\Wow6432Node\\Microsoft\Windows\CurrentVersion\Uninstall\{4AAC4B07-77EF-4BCF-88DC-D24E4DE683E8} Preinstalled.HPSupportAssistant Registry HKLM\Software\Wow6432Node\\Microsoft\Windows\CurrentVersion\Uninstall\{63F82052-C045-4F97-A3CA-C41D2CCA1FFA} Preinstalled.HPSureConnect Folder C:\Program Files\HPCOMMRECOVERY Preinstalled.HPSureConnect Registry HKLM\Software\Wow6432Node\\Microsoft\Windows\CurrentVersion\Uninstall\{6468C4A5-E47E-405F-B675-A70A70983EA6} Preinstalled.HPTouchpointAnalyticsClient Folder C:\ProgramData\HP\HP TOUCHPOINT ANALYTICS CLIENT Preinstalled.HPTouchpointAnalyticsClient Registry HKLM\Software\Microsoft\Windows\CurrentVersion\Uninstall\{E5FB98E0-0784-44F0-8CEC-95CD4690C43F} AdwCleaner[S00].txt - [6699 octets] - [20/06/2025 11:00:22] AdwCleaner[C00].txt - [2652 octets] - [20/06/2025 20:26:39] ########## EOF - C:\AdwCleaner\Logs\AdwCleaner[S01].txt ##########
-
redcat2025 replied to redcat2025's topic in Virus and Ransomware related questions# ------------------------------- # Malwarebytes AdwCleaner 8.5.1.601 # ------------------------------- # Build: 03-26-2025 # Database: 2025-04-04.3 (Cloud) # Support: https://www.malwarebytes.com/support # # ------------------------------- # Mode: Scan # ------------------------------- # Start: 06-20-2025 # Duration: 00:00:14 # OS: Windows 11 (Build 22631.5472) # Scanned: 32083 # Detected: 51 ***** [ Services ] ***** No malicious services found. ***** [ Folders ] ***** Adware.LoadMoney C:\ProgramData\Partner PUP.Optional.Legacy C:\Program Files (x86)\GreenTree Applications PUP.Optional.Legacy C:\ProgramData\Microsoft\Windows\Start Menu\Programs\ytd video downloader PUP.Optional.Legacy C:\ProgramData\ytd video downloader Rogue.ForcedExtension C:\ProgramData\apn ***** [ Files ] ***** No malicious files found. ***** [ DLL ] ***** No malicious DLLs found. ***** [ WMI ] ***** No malicious WMI found. ***** [ Shortcuts ] ***** No malicious shortcuts found. ***** [ Tasks ] ***** No malicious tasks found. ***** [ Registry ] ***** PUP.Adware.Heuristic HKCU\SOFTWARE\73112565121019169982456341533895351211514098520 PUP.Optional.Legacy HKCU\Software\APN PIP PUP.Optional.Legacy HKCU\Software\Microsoft\Windows\CurrentVersion\Explorer\StartupApproved\Run|Web Companion PUP.Optional.Legacy HKCU\Software\Myfree Codec PUP.Optional.Legacy HKLM\Software\Wow6432Node\Myfree Codec PUP.Optional.Legacy HKLM\Software\Wow6432Node\\Microsoft\Windows\CurrentVersion\Uninstall\{1a413f37-ed88-4fec-9666-5c48dc4b7bb7} PUP.Optional.SlimCleanerPlus HKCU\Software\Microsoft\Internet Explorer\DOMStorage\castplatform.com PUP.Optional.WebCompanion HKCU\Software\Lavasoft\Web Companion PUP.Optional.WebCompanion HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap\Domains\webcompanion.com PUP.Optional.YTDToolbar HKCU\Software\{DAF8B7E5-449D-4180-8281-10E536E597F2} PUP.Optional.YTDToolbar HKLM\Software\Wow6432Node\{DAF8B7E5-449D-4180-8281-10E536E597F2} ***** [ Chromium (and derivatives) ] ***** No malicious Chromium entries found. ***** [ Chromium URLs ] ***** No malicious Chromium URLs found. ***** [ Firefox (and derivatives) ] ***** No malicious Firefox entries found. ***** [ Firefox URLs ] ***** No malicious Firefox URLs found. ***** [ Hosts File Entries ] ***** No malicious hosts file entries found. ***** [ Preinstalled Software ] ***** Preinstalled.HPAudioSwitch Folder C:\Program Files (x86)\HP\HPAUDIOSWITCH Preinstalled.HPAudioSwitch Registry HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{BE7019B0-DF32-4A1C-B44F-4AC62685CD25} Preinstalled.HPAudioSwitch Registry HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\HPAudioSwitch Preinstalled.HPAudioSwitch Task C:\Windows\System32\Tasks\HPAUDIOSWITCH Preinstalled.HPCoolSense Folder C:\Program Files (x86)\HP\HP COOLSENSE Preinstalled.HPCoolSense Folder C:\Users\Pixel-PC\AppData\Local\HP\HP COOLSENSE Preinstalled.HPCoolSense Folder C:\Windows\System32\Tasks\HP\HP COOLSENSE Preinstalled.HPCoolSense Registry HKLM\Software\Classes\CLSID\{224695A4-BD5E-4C38-B354-A4C828E61BF7} Preinstalled.HPJumpStartApps Folder C:\Program Files (x86)\HP\HP JUMPSTART APPS Preinstalled.HPJumpStartApps Registry HKLM\Software\Wow6432Node\\Microsoft\Windows\CurrentVersion\Uninstall\HP JumpStart Apps Preinstalled.HPJumpStartBridge Folder C:\Program Files (x86)\HP\HP JUMPSTART BRIDGE Preinstalled.HPJumpStartLaunch Folder C:\Program Files (x86)\HP\HP JUMPSTART LAUNCH Preinstalled.HPJumpStartLaunch Registry HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tasks\{0B3EB0F5-EE46-4F08-B2BA-057B6F86AB15} Preinstalled.HPJumpStartLaunch Registry HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Schedule\TaskCache\Tree\HPJumpStartLaunch Preinstalled.HPJumpStartLaunch Task C:\Windows\System32\Tasks\HPJUMPSTARTLAUNCH Preinstalled.HPRegistrationService Folder C:\Program Files (x86)\HP\HP REGISTRATION SERVICE Preinstalled.HPRegistrationService Folder C:\ProgramData\HP\HP REGISTRATION SERVICE Preinstalled.HPSupportAssistant Folder C:\HP\SUPPORT Preinstalled.HPSupportAssistant Folder C:\Program Files (x86)\HEWLETT-PACKARD\HP CUSTOMER FEEDBACK Preinstalled.HPSupportAssistant Folder C:\Program Files (x86)\HEWLETT-PACKARD\HP SUPPORT FRAMEWORK Preinstalled.HPSupportAssistant Folder C:\Program Files (x86)\HEWLETT-PACKARD\HP SUPPORT SOLUTIONS Preinstalled.HPSupportAssistant Folder C:\ProgramData\HEWLETT-PACKARD\HP SUPPORT FRAMEWORK Preinstalled.HPSupportAssistant Folder C:\Users\Pixel-PC\AppData\Local\HEWLETT-PACKARD\HP SUPPORT FRAMEWORK Preinstalled.HPSupportAssistant Folder C:\Users\Pixel-PC\AppData\Roaming\HEWLETT-PACKARD\HP SUPPORT FRAMEWORK Preinstalled.HPSupportAssistant Folder C:\Windows\System32\config\systemprofile\AppData\Local\HEWLETT-PACKARD\HP SUPPORT FRAMEWORK Preinstalled.HPSupportAssistant Registry HKLM\Software\Classes\CLSID\{E76FD755-C1BA-4DCB-9F13-99BD91223ADE} Preinstalled.HPSupportAssistant Registry HKLM\Software\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{E76FD755-C1BA-4DCB-9F13-99BD91223ADE} Preinstalled.HPSupportAssistant Registry HKLM\Software\Wow6432Node\\Classes\CLSID\{E76FD755-C1BA-4DCB-9F13-99BD91223ADE} Preinstalled.HPSupportAssistant Registry HKLM\Software\Wow6432Node\\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{E76FD755-C1BA-4DCB-9F13-99BD91223ADE} Preinstalled.HPSupportAssistant Registry HKLM\Software\Wow6432Node\\Microsoft\Windows\CurrentVersion\Uninstall\{4AAC4B07-77EF-4BCF-88DC-D24E4DE683E8} Preinstalled.HPSupportAssistant Registry HKLM\Software\Wow6432Node\\Microsoft\Windows\CurrentVersion\Uninstall\{63F82052-C045-4F97-A3CA-C41D2CCA1FFA} Preinstalled.HPSureConnect Folder C:\Program Files\HPCOMMRECOVERY Preinstalled.HPSureConnect Registry HKLM\Software\Wow6432Node\\Microsoft\Windows\CurrentVersion\Uninstall\{6468C4A5-E47E-405F-B675-A70A70983EA6} Preinstalled.HPTouchpointAnalyticsClient Folder C:\ProgramData\HP\HP TOUCHPOINT ANALYTICS CLIENT Preinstalled.HPTouchpointAnalyticsClient Registry HKLM\Software\Microsoft\Windows\CurrentVersion\Uninstall\{E5FB98E0-0784-44F0-8CEC-95CD4690C43F} ########## EOF - C:\AdwCleaner\Logs\AdwCleaner[S00].txt ##########
-
Hello @booger, Welcome! (please) Read before you create a new topic! Open KIS, select Settings, select Additional, uncheck Enable Secure Keyboard Input, select Save, select Save (to confirm the action). 💥 However, there’s also a tiny Quick launch keyboard icon that generates a Secure Keyboard Input is enabled popup → image 4, that drives many Kaspersky subscribers nuts, that cannot be disabled or managed in any way, discussed in topic raised by @Killeriguana How do I disable the "Secure Keyboard Input is enabled" pop-up WITHOUT disabling the Secure Input feature itself? Thank you🙏 Flood🐳+🐋 References: Secure Keyboard Input About protection of personal data on the Internet How to configure protection of data entered on the computer keyboard
-
 rbmancini posted a topic in Virus and Ransomware related questionsOperating System: Windows 10 Pro (version 22H2) Kaspersky Application: Kaspersky Plus Issue: Application blocked or disrupted due to false positive detection Hello, I’m experiencing issues using a legitimate application called KeyPress OSD. It’s an open-source tool that displays on-screen keyboard and mouse input, which is particularly useful for recording tutorial videos where viewers need to see which shortcuts I’m using. Unfortunately, Kaspersky Plus flags or blocks it, likely because it's built with AutoHotkey (AHK) — a scripting language that’s often wrongly identified as malicious. The tool is completely safe and widely used in educational contexts. 🔗 AutoHotkey forum thread about false positives: https://www.autohotkey.com/boards/viewtopic.php?f=17&t=62266 Product Description: KeyPress OSD is an On-Screen Display for key and mouse inputs. It shows key presses in large text on-screen, ideal for accessibility, streaming, or tutorials. It uses AutoHotkey as its scripting engine, which sometimes triggers antivirus alerts. What I'm looking for: How can I configure Kaspersky Plus to allow this app to run normally? Is there a recommended way to exclude a trusted AutoHotkey-based app from scans or monitoring? Should I whitelist the .EXE file, the folder, or the AutoHotkey interpreter itself? If needed, I can attach screenshots showing the detection pop-up or logs. I’m happy to follow all safety best practices, but I also need to be able to use this tool for my work without constant interruptions. Thanks in advance for your support! Best regards, Rafael